
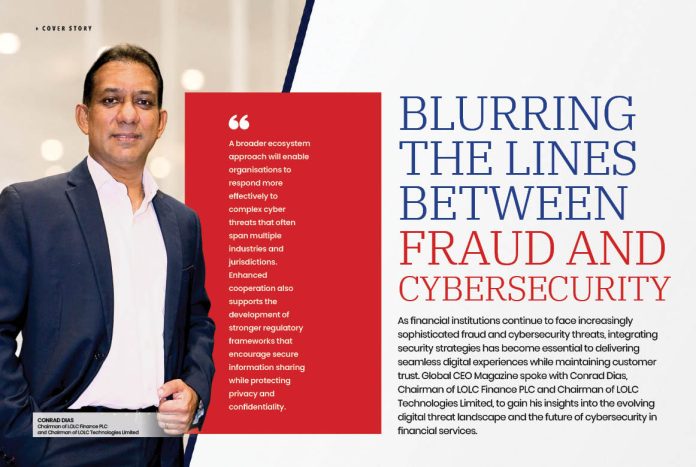
As financial institutions continue to face increasingly sophisticated fraud and cybersecurity threats, integrating security strategies has become essential to delivering seamless digital experiences while maintaining customer trust. Global CEO Magazine spoke with Conrad Dias, Chairman of LOLC Finance PLC and Chairman of LOLC Technologies Limited, to gain his insights into the evolving digital threat landscape and the future of cybersecurity in financial services.
As financial institutions continue to expand their digital services, how has the cyber threat landscape evolved, and what are the most significant digital fraud risks facing customers today?
When we consider today’s digital environment, the threat landscape has shifted significantly towards human centric attacks. In other words, cybercriminals are increasingly exploiting human behaviour through social engineering rather than relying solely on technical vulnerabilities. This evolution has been particularly evident within the financial services sector, driven largely by the rapid adoption of digital technologies and digital financial services.
Today, financial institutions have little choice but to embrace technology and digitally transform. Organisations that fail to do so risk losing their competitive advantage and may even face an existential threat. Whether in finance companies, financial services or the banking sector, technology has become the foundation of the industry. Financial services have evolved into technology driven businesses rather than traditional brick-and-mortar operations. Consequently, adopting digital technologies has become essential to meeting evolving customer expectations and remain relevant.
As a result, most financial institutions have implemented advanced technological controls to prevent and detect fraud as part of their broader digital transformation strategies.
Fraud, however, is a broad and multifaceted concept that encompasses numerous attack methods and techniques. From a digital fraud and cybersecurity perspective, the most significant change has been the transition from predominantly technology-driven attacks to human-centric attacks. While many technology-based threats can be effectively mitigated through robust technical controls, attacks that manipulate human behaviour through social engineering continue to present a far more complex and evolving challenge.
Examples of this trend include account takeover attacks, password sharing and the misuse of one-time passwords (OTPs). Although technologies such as OTP based authentication have significantly enhanced security, customers continue to share these codes with fraudsters, making human behaviour the weakest link in the security chain.
As financial institutions continue to introduce secure payment platforms, QR code payments and a wide range of digital financial services, technology adoption has become indispensable. Nevertheless, cybercriminals are adapting just as quickly. Rather than attempting to defeat sophisticated security technologies directly, they increasingly exploit human trust, emotions and behavioural weaknesses.
This changing threat landscape highlights the need to complement technological controls with comprehensive customer awareness programmes, employee education and continuous initiatives aimed at reducing the success of social engineering attacks.
Ultimately, cybersecurity is no longer solely about protecting systems and networks. It is equally about protecting people. As financial services continue to become more digital, organisations must invest not only in advanced technologies but also in building a strong security culture among employees and customers. Only by combining technological resilience with informed and vigilant users can financial institutions effectively reduce digital fraud risks and strengthen customer confidence in an increasingly connected financial ecosystem.
The financial sector is increasingly being targeted by cybercriminals. What are the key measures financial institutions should implement to prevent, detect and respond to digital fraud, phishing attacks and other cyber threats?
Fraud prevention is a multifaceted challenge that cannot be addressed by any organisation in isolation. It requires a coordinated approach that combines technology, robust processes and close collaboration among multiple stakeholders.
The first priority is prevention, which involves implementing a comprehensive range of security technologies and controls. One of the most fundamental principles that organisations should adopt is the Zero Trust security model. This has become a cornerstone of modern cybersecurity strategies because it is based on a simple but powerful principle: never automatically trust any user, device or system. Instead, every access request must be continuously verified and validated before permission is granted.
Accordingly, organisations should establish a Zero-Trust framework as a foundational element of their cybersecurity strategy. Beyond this, financial institutions should implement additional protective measures such as multifactor authentication (MFA). Rather than relying solely on a username and password, MFA requires users to verify their identity through multiple authentication methods, such as a password combined with a one time password (OTP) or biometric verification. This significantly reduces the likelihood of unauthorised access.
However, technology alone is not sufficient. Employee awareness and customer education remain equally important pillars of an effective fraud prevention strategy. Regular awareness programmes help individuals recognise cyber threats, adopt safe digital practices and reduce the likelihood of successful social engineering attacks.
The second critical component is detection. Organisations must develop the capability to identify whether they are under attack, whether their security controls have been compromised or whether vulnerabilities exist within their environment. Strong detection capabilities enable organisations to identify threats at an early stage and respond before significant damage occurs.
Modern cybersecurity has shifted from asking whether an organisation has been breached to assuming that a breach may already have occurred. This philosophy, commonly referred to as the assume breach approach, encourages organisations to focus on identifying potential compromises quickly and implementing effective mitigation measures rather than waiting for confirmation that an incident has taken place.
By adopting this mindset, organisations strengthen their resilience and improve their ability to detect, respond to and recover from cyber incidents. This is particularly important for financial institutions, where operational continuity and customer confidence are paramount.
Security Operations Centres (SOCs) have therefore become an essential part of the cybersecurity framework within banks and financial institutions. These centres continuously monitor systems, analyse security events and coordinate rapid responses to potential cyber threats, thereby enhancing organisational resilience and protecting critical infrastructure and customer data.
In addition to established security controls, organisations should increasingly leverage advanced technologies such as artificial intelligence-driven fraud detection, behavioural analytics and continuous monitoring solutions. These technologies enable financial institutions to identify unusual patterns, detect suspicious activities and respond proactively to emerging threats while maintaining a seamless customer experience.
Equally important is the organisation’s ability to respond effectively when a security incident occurs. Operating under an assume breach philosophy requires organisations to establish comprehensive and well-tested incident response plans before an attack takes place. Waiting until after an incident has occurred to develop response mechanisms inevitably delays recovery and increases operational and reputational risks.
Every organisation should therefore maintain a comprehensive incident response strategy supported by a robust crisis management framework. This commitment must extend beyond the information technology function and be fully endorsed by senior management and the board of directors. Executive leadership plays a critical role in ensuring that the organisation is prepared to respond decisively during a cyber crisis.
Experience has shown that many organisations suffer greater damage not because of the cyber attack, but because their response plans are inadequate or poorly executed. Weak governance, unclear responsibilities and ineffective crisis management often amplify the consequences of an incident.
The key message is that cybersecurity is no longer solely an information technology responsibility. It has evolved into an enterprise-wide business discipline that requires the active involvement, accountability and collaboration of every level of the organisation. Building cyber resilience is therefore not simply about deploying better technology. It requires strong leadership, sound governance, continuous vigilance and a culture in which cybersecurity is recognised as a shared organisational responsibility.
As digital banking and financial services become more accessible, how can institutions effectively balance customer convenience with robust cybersecurity and fraud prevention measures?
One of the greatest challenges facing financial institutions today is ensuring that strong security measures do not come at the expense of customer experience.
In a Zero Trust environment, where no user or transaction is automatically trusted and every interaction requires authentication and authorisation, organisations must carefully balance security with usability. Excessive security checks can create unnecessary friction, resulting in inconvenience for customers and potentially discouraging the use of digital services.
Customers expect financial institutions to provide both robust security and a seamless digital experience. Achieving this balance is one of the most significant challenges organisations face as digital financial services continue to evolve.
A practical way to address this challenge is by adopting a risk-based security approach. Rather than applying identical security controls to every transaction, organisations should assess the level of risk associated with each interaction and implement security measures that are proportionate to that risk.
For example, a routine low value transaction, such as making a payment of one thousand rupees, should not require the same level of verification as transferring one million rupees. A risk-based approach enables financial institutions to provide customers with a smooth and convenient experience for low-risk activities while applying enhanced authentication and additional security controls for higher value or higher risk transactions.
This principle recognises that different transactions require different levels of protection. Customers making everyday purchases expect speed and convenience, much like a simple contactless card payment. Conversely, when transferring substantial amounts of money, customers generally appreciate additional verification because it provides reassurance that the transaction is secure and is being made to the intended recipient.
From a technical perspective, this approach is commonly referred to as adaptive authentication. Adaptive authentication dynamically adjusts the level of verification required by analysing contextual factors such as transaction value, customer behaviour, device information, location and other security indicators. This enables organisations to strengthen protection where necessary while minimising unnecessary disruption for legitimate users.
At the same time, customers must have confidence that their personal information and financial transactions are secure. Ideally, the underlying security mechanisms should remain largely invisible throughout the customer journey. The most effective security is often the security that customers do not consciously notice. They should simply feel confident that appropriate protections are operating seamlessly in the background without creating unnecessary complexity or repeated authentication requests.
Looking ahead, emerging technologies will play an increasingly important role in achieving this balance. Biometric authentication has already become a key component of secure digital banking. Mobile platforms, including Android and Apple’s ecosystem, now provide sophisticated biometric capabilities that offer both enhanced security and greater convenience.
The banking industry should continue integrating these technologies into its digital services. Biometric authentication, combined with adaptive security controls and intelligent risk assessment, enables financial institutions to strengthen customer protection while delivering a faster, simpler and more intuitive digital experience.
As digital banking continues to evolve, technologies such as visual intelligence, advanced authentication and contextual security will become increasingly important in delivering personalised, secure and frictionless banking experiences.
What role do emerging technologies such as artificial intelligence, machine learning, behavioural analytics and real-time transaction monitoring play in strengthening cybersecurity and fraud detection across the financial services industry?
Artificial intelligence (AI) has become one of the most transformative technologies of our time. While it offers tremendous opportunities for innovation and operational efficiency, it is also becoming increasingly accessible to cybercriminals, who are using it to enhance the sophistication and scale of their attacks.
At the same time, AI has become an indispensable tool in strengthening cybersecurity. Machine learning, in particular, is already being widely deployed to detect fraud, identify anomalies and recognise suspicious activities that may otherwise remain unnoticed.
One of the most valuable applications of AI within financial services is behavioural analytics. Every digital interaction conducted through mobile applications, internet banking platforms and other digital channels generates valuable behavioural data. By analysing this information, financial institutions can better understand normal customer behaviour, identify emerging risks and respond proactively to potential threats.
Behavioural analytics enables organisations to establish patterns based on how customers typically conduct their financial activities. Transaction values, frequency of transactions, preferred devices, login locations and usage habits all contribute to building a behavioural profile. When customer activity deviates significantly from these established patterns, the system can identify the anomaly and trigger additional security measures.
For example, if a customer who normally accesses online banking from Colombo suddenly attempts to log in from multiple geographically distant locations within a short period, the system can immediately recognise this as unusual behaviour requiring further investigation. Likewise, if a customer who generally performs low value transactions suddenly initiates several unusually large transfers, the system can automatically trigger additional authentication before allowing the transactions to proceed.
This intelligent analysis enables financial institutions to detect fraud at a much earlier stage while maintaining a seamless experience for legitimate customers. The objective is not simply to strengthen security but also to build digital trust by giving customers confidence that suspicious activities are being continuously monitored and managed.
Real-time fraud intelligence platforms further enhance these capabilities by continuously monitoring customer transactions, identifying behavioural changes and detecting emerging threats as they occur. These systems enable financial institutions to respond immediately by applying adaptive security controls, requesting additional authentication or temporarily suspending suspicious transactions until they can be verified.
Artificial intelligence therefore serves two equally important purposes. It strengthens fraud prevention while allowing financial institutions to maintain the high level of convenience that customers expect from modern digital banking.
However, organisations must also recognise that cybercriminals are leveraging the same technologies. AI is becoming an increasingly powerful tool for creating sophisticated phishing attacks, automating malicious activities and identifying new vulnerabilities. Consequently, financial institutions must continue investing in AI-driven cybersecurity solutions that evolve at the same pace as the threats they are designed to combat.
The future of cybersecurity will increasingly depend on intelligent technologies that can learn, adapt and respond in real time. By combining artificial intelligence, machine learning, behavioural analytics and continuous transaction monitoring, financial institutions will be better equipped to protect customers, reduce fraud and strengthen trust across the rapidly evolving digital financial ecosystem.
Customer awareness is often considered the first line of defence against cybercrime. What best practices should financial institutions adopt to educate customers on digital security and safe online financial behaviour?
Customer awareness remains one of the most important pillars of cybersecurity. Regardless of how advanced a financial institution’s security technologies may be, customers themselves continue to play a critical role in protecting against cyber threats.
Even today, many individuals fall victim to scams by disclosing sensitive information, such as one time passwords (OTPs), despite repeated warnings never to share them. This clearly demonstrates how cybercrime has evolved from predominantly technology-driven attacks to human-centric attacks that exploit trust, emotions and behavioural vulnerabilities.
For this reason, cybersecurity awareness must become a shared responsibility. Financial institutions, educational institutions, regulators and the wider community all have an important role to play in promoting safe digital practices. Through social media campaigns, public awareness initiatives, educational programmes and regular customer engagement, organisations can help individuals recognise cyber threats and make informed decisions when conducting financial transactions online.
Customer education should not be treated as a one-off initiative. As cybercriminals continuously adapt their methods, awareness programmes must also evolve to address emerging threats, including phishing, identity theft, social engineering and fraudulent digital payment schemes. Regular communication helps customers remain alert and reinforces safe online behaviour.
Ultimately, customer awareness is both the first line of defence and a critical component in building a secure digital ecosystem. Cybersecurity is a shared responsibility between financial institutions and their customers. While organisations must implement robust security frameworks and advanced technological controls, customers also have a vital role in protecting their own digital identities and financial information.
Without informed and vigilant customers, even the most sophisticated security systems cannot completely eliminate cyber risks. A secure digital environment can only be achieved through a collective effort, where financial institutions and customers work together to identify risks, adopt secure practices and remain vigilant against evolving cyber threats.
With the rapid growth of digital lending, mobile applications, online payments and other digital financial services, what additional safeguards are becoming essential to protect customer information and transactions?
One of the most important safeguards is the adoption of responsible data management and data-sharing practices. As personal data protection regulations, including Sri Lanka’s Personal Data Protection Act (PDPA), come into effect, organisations must strengthen the way they collect, store, manage, protect and use customer information.
However, responsible data management should extend beyond regulatory compliance. It requires organisations to build a culture in which customer privacy and information security are embedded throughout their operations. Although the banking sector has made significant progress in this area, greater awareness and stronger governance are still needed across the broader digital ecosystem.
Alongside robust governance frameworks, financial institutions should leverage advanced technologies such as digital identity platforms and secure identity verification solutions. These technologies enhance customer authentication, strengthen security and build greater trust in digital financial services.
A particularly important priority for Sri Lanka is the development of a comprehensive verifiable national digital identity framework. Such a framework would significantly improve digital Know Your Customer (KYC) processes by enabling secure, reliable and fully digital customer verification. Although digital banking platforms have advanced considerably, the underlying digital identity infrastructure has yet to evolve sufficiently to support seamless end-to-end verification. Strengthening this foundation will be essential for the continued growth of secure digital financial services.
Technologies such as tokenisation also offer significant benefits. By replacing sensitive banking information with secure digital tokens during transactions, tokenisation reduces the risk of exposing confidential customer data while enhancing trust in digital payment platforms.
Another promising development is LankaPay’s Payment Exchange Name (PEN) initiative for bank accounts. This approach enables customers to conduct transactions using their registered mobile numbers rather than directly sharing bank account details. Similar to India’s Unified Payments Interface (UPI), such a system can improve convenience while reducing the exposure of sensitive financial information.
As financial institutions increasingly rely on Application Programming Interfaces (APIs) to deliver integrated digital services, API security has also become a critical priority. Secure API architecture, continuous monitoring and robust authentication controls are essential to protect customer information and maintain confidence in interconnected financial systems.
Ultimately, protecting customer information requires far more than implementing individual security technologies. It demands a comprehensive strategy that combines strong governance, advanced technological safeguards, secure digital identity frameworks, responsible data management and continuous innovation. By strengthening these foundations, financial institutions can build a more resilient digital ecosystem while maintaining the trust and confidence of their customers.
When a cyber incident or suspected fraudulent activity occurs, what are the key elements of an effective incident response strategy to minimise customer impact and ensure operational resilience?
An effective incident response strategy begins long before a cyber incident occurs. Organisations must proactively prepare themselves to detect threats rapidly, contain incidents effectively, recover quickly and continuously learn from each event. These four elements form the foundation of a resilient cybersecurity framework.
A key principle underpinning modern cybersecurity is the assume breach approach. Rather than operating on the assumption that systems are secure until proven otherwise, organisations should prepare for the possibility that a compromise may already have occurred. This mindset enables them to develop robust response capabilities before an incident takes place, significantly improving their ability to minimise disruption and recover swiftly.
Building cyber resilience requires continuous preparedness, well-defined response processes and a commitment to ongoing improvement. Financial institutions should establish dedicated incident response teams supported by strong governance and oversight from senior management and the board of directors. Cyber resilience is no longer solely a technical responsibility; it is a leadership priority that requires strategic direction and organisational commitment.
One of the most critical aspects of incident response is effective communication. During a cybersecurity incident, organisations must communicate promptly, transparently and accurately with customers, regulators, business partners and the wider public. Clear communication helps maintain confidence, reduces uncertainty and demonstrates accountability during what can often be a highly sensitive situation.
Whether an incident involves cybercrime, data theft or internal fraud, restoring and maintaining customer trust must remain the highest priority. Banking has always been built on trust, and this principle becomes even more important in an increasingly digital environment where customers interact primarily with technology rather than
face-to-face with employees.
Maintaining confidence requires financial institutions to demonstrate not only strong security but also operational resilience. Organisations must be capable of detecting incidents quickly, containing their impact, restoring services efficiently and continuously strengthening their defences through lessons learnt from previous events.
An important element of resilience planning is the establishment of measurable recovery objectives. Metrics such as the Recovery Time Objective (RTO), Recovery Point Objective (RPO) and Mean Time To Recover (MTTR) provide valuable benchmarks for assessing how quickly services can be restored, how much data loss can be tolerated and how effectively business operations can continue following a disruption.
These objectives are typically incorporated into Business Continuity Planning (BCP) and Disaster Recovery (DR) frameworks, enabling organisations to minimise operational disruption while safeguarding customer confidence.
Ultimately, effective incident response extends beyond technology. It requires strong leadership, disciplined governance, comprehensive planning and a culture of continuous improvement. Financial institutions that invest in these capabilities will be better positioned to respond decisively to cyber incidents while preserving customer trust and ensuring long-term operational resilience.
How important is collaboration among regulators, financial institutions, technology providers and law enforcement agencies in strengthening the country’s cybersecurity ecosystem and combating digital fraud?
Collaboration has become one of the most important requirements for strengthening national cybersecurity. Cybercriminals rarely operate in isolation. They function within highly organised networks, often using the dark web to exchange stolen information, share attack techniques and coordinate sophisticated cyber operations across international borders.
To counter these increasingly organised threats, the cybersecurity community must adopt an equally collaborative approach. Regulators, financial institutions, technology providers, telecommunications companies and law enforcement agencies must work together by sharing intelligence, coordinating responses and developing collective defence strategies.
Sri Lanka has already established important institutions and initiatives, including the Sri Lanka Computer Emergency Readiness Team (Sri Lanka CERT) and sector specific cybersecurity frameworks. These have made valuable contributions towards strengthening the country’s cyber resilience. However, there remains considerable scope to improve information sharing, coordination and real-time collaboration among stakeholders.
Encouragingly, initiatives are currently under way to strengthen fraud management within Sri Lanka’s banking sector through a more coordinated national framework. Such initiatives are expected to improve intelligence sharing, accelerate incident response and enhance collective protection against emerging financial threats.
Nevertheless, collaboration should extend beyond the traditional banking ecosystem. Preventing digital fraud requires the active participation of multiple sectors, including telecommunications providers, the Telecommunications Regulatory Commission, payment service providers, technology companies and specialised law enforcement agencies such as the Cyber Crimes Division.
A broader ecosystem approach will enable organisations to respond more effectively to complex cyber threats that often span multiple industries and jurisdictions. Enhanced cooperation also supports the development of stronger regulatory frameworks that encourage secure information-sharing while protecting privacy and confidentiality.
Although cybercriminals represent only a small minority, they frequently benefit from extensive collaboration within their own networks. The collective strength of governments, regulators, financial institutions, technology providers and citizens is therefore essential to creating a more effective defence against digital crime.
Ultimately, cybersecurity is a shared national responsibility. No single organisation possesses all the expertise, intelligence or resources required to combat today’s sophisticated cyber threats. Success depends on building trusted partnerships, strengthening communication channels and fostering a culture of collaboration across both the public and private sectors.
By working together, stakeholders can create a stronger, more resilient cybersecurity ecosystem that not only protects financial institutions but also safeguards customers, strengthens digital trust and supports the continued growth of Sri Lanka’s digital economy.
Data privacy and information security are fundamental to maintaining customer trust. What governance frameworks and industry best practices should financial institutions adopt to safeguard sensitive customer information?
Data privacy has become one of the most significant priorities in today’s digital landscape. With Sri Lanka’s Personal Data Protection Act (PDPA) expected to come into effect, organisations must strengthen their approach to responsible data management, privacy protection and governance.
Data protection should not be regarded solely as an information technology function. It is an enterprise-wide risk management responsibility that requires the active involvement of every part of the organisation. Building a strong data governance framework is therefore essential. This should include clearly-defined data ownership, information classification, access management and appropriate security controls to ensure that sensitive customer information is handled securely throughout its lifecycle.
A structured approach to data governance not only helps organisations comply with regulatory requirements but also reduces operational risks and strengthens customer confidence in digital services.
Within the banking and financial services sector, the Technology Risk Management and Resilience (TRMR) Framework issued by the Central Bank of Sri Lanka provides important guidance for strengthening technology risk management and cybersecurity resilience. In addition, internationally-recognised standards such as ISO/IEC 27001 offer comprehensive frameworks for establishing effective information security management systems.
However, organisations should not treat these standards merely as compliance requirements or checklist exercises. The real value lies in embedding these frameworks into everyday business operations so that they become part of the organisational culture and contribute meaningfully to resilience and operational excellence.
Another important principle is the adoption of security by design and privacy by design. Rather than introducing security and privacy controls after systems have been developed or deployed, organisations should integrate these principles from the earliest stages of planning, design and implementation. Embedding security into systems from the outset enables organisations to respond more effectively to evolving cyber risks while building more resilient digital services.
Looking ahead, Sri Lanka must encourage greater adoption of cyber insurance as an additional risk management tool. Although cyber insurance remains relatively limited in availability and affordability, it offers significant potential to help organisations manage the financial consequences of cyber incidents and strengthen overall organisational resilience.
Ultimately, maintaining customer trust depends on far more than regulatory compliance. It requires a comprehensive governance framework supported by strong leadership, internationally-recognised standards, embedded security practices and a culture that recognises data protection as a strategic business priority.
Looking ahead, what do you see as the key priorities for the financial services industry in strengthening cybersecurity, fraud prevention and digital resilience as digital financial services continue to evolve?
The pace of technological advancement, particularly in the field of artificial intelligence (AI), continues to accelerate. As cyber threats become increasingly sophisticated, it is becoming more challenging for individual organisations to keep pace with the rapidly evolving threat landscape.
To address these challenges, financial institutions must continue strengthening their cyber defence capabilities by leveraging AI-powered security solutions that can detect, analyse and respond to threats more quickly and accurately than traditional approaches.
At the same time, organisations should continue implementing Zero Trust architecture while embracing the principle of fraud prevention by design, ensuring that security controls are integrated into systems, products and processes from the very beginning rather than being added later. Together, these approaches provide a stronger foundation for secure and resilient digital financial services.
Looking further ahead, financial institutions must also prepare for the emergence of quantum computing. Although still in its early stages, quantum technology has the potential to fundamentally reshape the cybersecurity landscape. Traditional cryptographic methods that currently protect digital financial systems may eventually become vulnerable to quantum computing capabilities.
Consequently, organisations should begin evaluating quantum resistant cryptography and other emerging security technologies to strengthen long-term cyber resilience. Just as artificial intelligence is becoming increasingly accessible to both legitimate organisations as well as cybercriminals, quantum computing may also become a powerful tool for malicious actors in the future. Preparing now will help financial institutions remain resilient as these technologies mature.
Research into quantum-based cybersecurity solutions is already under way, making it essential for organisations to monitor developments, evaluate emerging technologies and invest strategically in future- ready security capabilities. More broadly, the financial services industry must adopt a forward-looking approach to cybersecurity. Cybersecurity should no longer be viewed simply as a technical function or a regulatory obligation. Instead, it should be recognised as a strategic business enabler that supports innovation, operational resilience and long-term customer trust.
Financial services have become increasingly technology-driven, and this transformation is expected to accelerate further with future developments such as Central Bank Digital Currencies (CBDCs). As the movement of money becomes almost entirely digital, cybersecurity will become even more fundamental to ensuring the security, reliability and continuity of digital financial ecosystems. Organisations must therefore embed cybersecurity into their core business strategy rather than treating it as a compliance exercise. Investment in technology, governance, innovation and people must continue to evolve alongside emerging threats.
Ultimately, the future of financial services will depend not only on digital innovation but also on the industry’s ability to inspire confidence in the digital economy. Institutions that successfully integrate cybersecurity into every aspect of their business will be better positioned to protect customers, strengthen resilience and build the trust that underpins sustainable growth in an increasingly connected world.
